
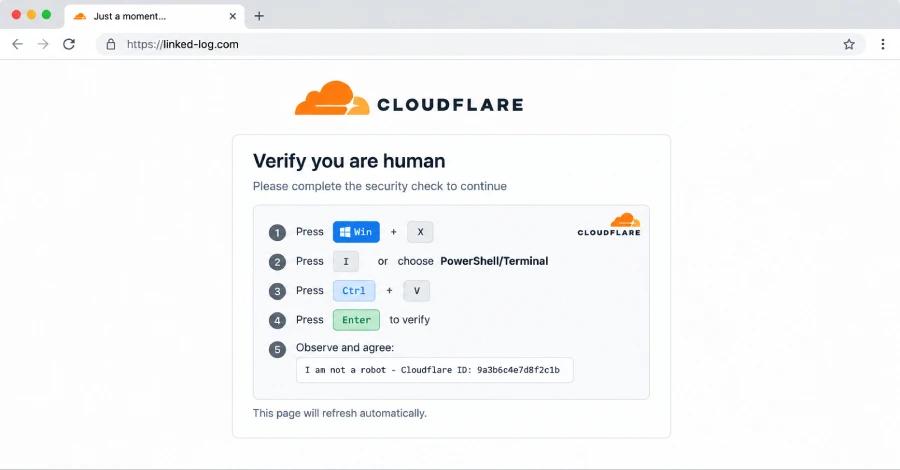
Microsoft’s threat researchers have disclosed a new variation on the ClickFix social-engineering technique, called TerminalFix, that uses fake Cloudflare CAPTCHA pages to trick website visitors into running a malicious PowerShell command. Unlike earlier ClickFix campaigns that steer victims to the Windows Run dialog, TerminalFix sends users to Windows Terminal or PowerShell — where multi-line scripts execute more reliably and draw less suspicion.
Attacks begin on compromised websites. A visitor is shown a convincing Cloudflare verification overlay, the same kind that blocks bots on legitimate services. The overlay instructs the user to copy a command and paste it into PowerShell to “verify” themselves. Executing that command kicks off a multi-stage chain: the script downloads a ZIP containing a legitimate Windows binary bundled with a rogue DLL, which sideloads itself, then fetches additional payloads hidden inside PNG images hosted on attacker-controlled domains. A Python-based reverse-tunnel implant is deployed, opening an encrypted WebSocket channel back to attacker infrastructure and giving the intruder persistent, direct access to the victim’s internal network — not just the infected machine. Active Directory reconnaissance runs in parallel, positioning the attacker for lateral movement, privilege escalation, data exfiltration, and potential ransomware deployment.
Microsoft recommends organizations restrict PowerShell and Run dialog access for standard users via AppLocker, Application Control for Windows, or Group Policy; monitor endpoint telemetry for DLL sideloading indicators; and enable PowerShell script block logging to detect obfuscated commands. Training employees to recognize ClickFix-style prompts is highlighted as a critical preventive control.