
Researchers at Check Point have uncovered a sustained campaign targeting Brazilian government and educational institutions. A Chinese-speaking cybercrime cluster they call Gambling Goblin has been compromising web servers and installing rogue Apache modules — software that runs inside the web server itself — to intercept incoming visitors and silently route them to attacker-controlled gambling and sports betting pages.
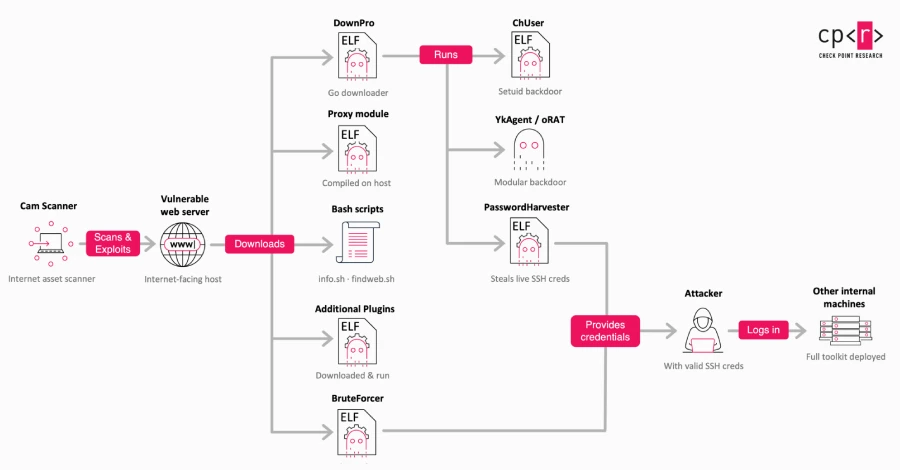
The attack is subtle by design. The compromised site keeps its normal domain and SSL certificate, so browser address bars show nothing alarming. The malicious module strips out the real site’s security headers, injects the gambling content, and proxies it back to visitors without revealing the redirect. Check Point says the group has operated this way since at least mid-2025, targeting .gov.br portals belonging to Brazilian municipalities and police forces, as well as university hosts. The likely motive is search engine optimization manipulation: high-trust government and academic domains push the gambling pages up in search rankings. In addition to the redirect module, the attackers leave behind a full toolkit — a custom downloader (DownPro), a modular backdoor (AlphaAgent), a remote access trojan (oRAT), an SSH credential stealer, and a brute-forcing tool for further lateral movement.
Brazil only began licensing fixed-odds betting in January 2025, so a wave of new gambling sites seeking visibility in Brazilian search results provides a plausible financial motive. Check Point has not confirmed whether the promoted betting sites are among the country’s licensed operators.