
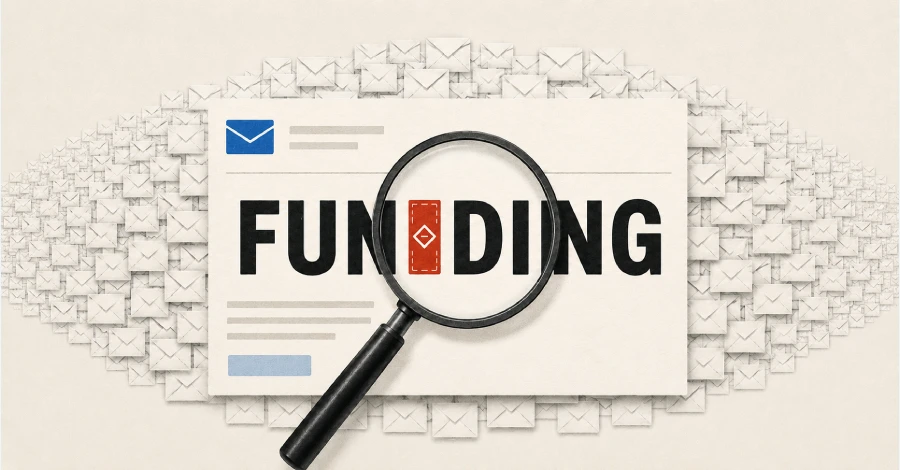
A large-scale phishing operation has been inserting invisible Unicode characters inside ordinary-looking financial keywords to evade email filters and land in inboxes that would otherwise reject the messages. Microsoft, which tracked the campaign, calls the trick “ASCII smuggling” — and it exploits a block of Unicode code points (U+E0000 to U+E007F) that human interfaces never render, making the text look perfectly normal to a reader while confusing detectors scanning for keyword or regex matches.
In practice, a word like “funding” becomes “fun[invisible]ding” — the reader sees nothing unusual, but a filter matching the literal string “funding” finds no contiguous sequence and lets the message through. The campaign first emerged in early February 2026 and ran at high volume through mid-May, sending between one and 2.37 million messages on peak weekdays, almost always routed through the legitimate ActiveCampaign marketing platform. Using a trusted sending service gave the emails the IP reputation and authentication signals that reputation-based filters typically look for, making detection harder still. The activity is linked to a broader fraud ring targeting U.S. Small Business Administration loan applicants with AI-generated lures designed to harvest business and financial data for follow-on spear-phishing.