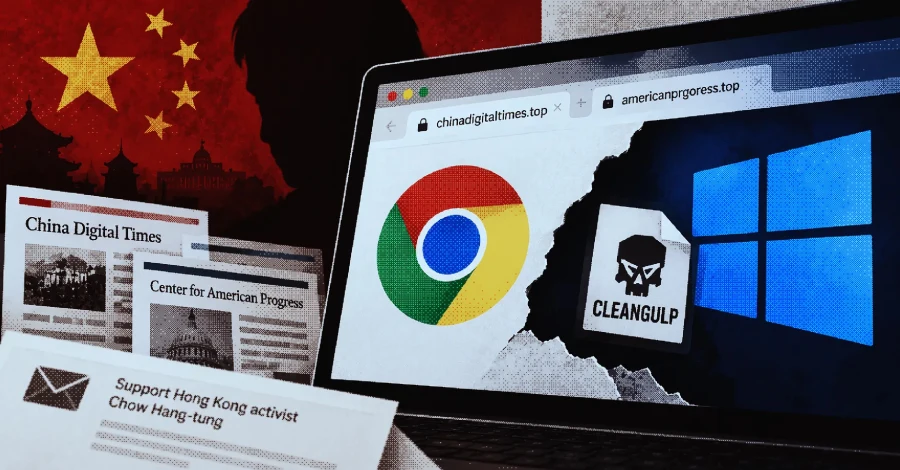
A Chinese threat actor tracked as UTA0565 built fake websites impersonating NGOs and media outlets to deliver a three-vulnerability exploit chain at government targets across Asia. Volexity researchers Damien Cash and Tom Lancaster, publishing their findings September 21, traced attacks detected September 3 and 4 to the same “BlueMoon” exploit kit used by several other Chinese groups — combining two Chrome V8 flaws (CVE-2026-85046 and CVE-2026-87491) with a Windows Advanced Local Procedure Call bug (CVE-2026-85880) to break out of Chrome’s sandbox and achieve remote code execution.
The campaign that Volexity analyzed in detail targeted Asian government entities with phishing emails written in Chinese and English, claiming to solicit support for Hong Kong activist Chow Hang-tung and masquerading as the Center for American Progress. Victims who clicked through reached a “config.html” page that silently triggered the exploit chain, ultimately dropping a previously undocumented malware family called CLEANGULP — a MSVC-compiled Windows implant that uses a typosquatted domain (thecovnresation[.]com, mimicking theconversation.com) for command-and-control over HTTP. Volexity says the wide adoption of BlueMoon across multiple Chinese espionage groups suggests the kit was centrally shared and customized within that community, and that the two organizations reporting so far likely represent only a fraction of the actual victim set.