
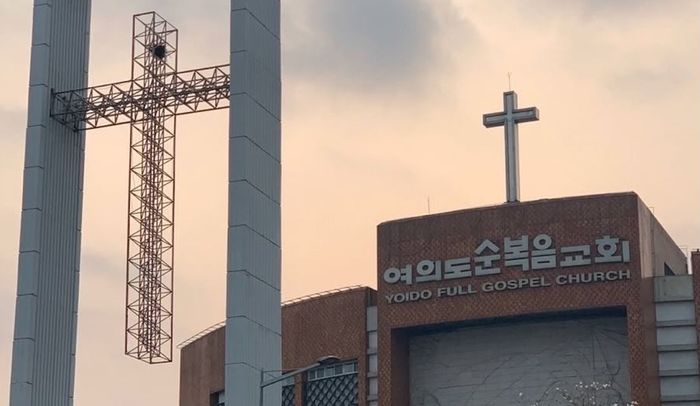
Two of South Korea’s largest Protestant churches, Seoul-based Yoido Full Gospel Church and SaRang Church, are investigating cyberattacks that may have exposed sensitive information about hundreds of thousands of members. The incidents surfaced after South Korean security firm Oasis Security published research this week analysing data recovered from a server used by the attackers. Yoido Full Gospel said it had identified one dataset tied to about 850,000 members and had been notified by South Korea’s internet security agency of a suspected breach; SaRang Church confirmed an investigation but has not said how many people are affected.
Oasis, which did not name the churches in its report, describes two separate intrusions that likely happened in August. In one, attackers installed a web shell, gained administrator-level access and copied more than 47 GB of data: membership records, payroll and accounting files, internal messages, employee login credentials and a network storage system holding reports and backups. In the other, they used previously leaked passwords and flaws in internal applications (some of which allowed resetting other users’ passwords) to reach the organization’s SAP system, exposing records tied to about 89,000 members, HR files for 286 employees including the senior pastor, and data on a college ministry’s students and staff. Oasis found the attackers reused infrastructure from an earlier compromise of an unnamed U.S.-based Christian content platform, and saw evidence they used AI to analyse vulnerabilities and software, move through networks and extract data. It did not identify the attackers or establish why religious organizations were targeted.