
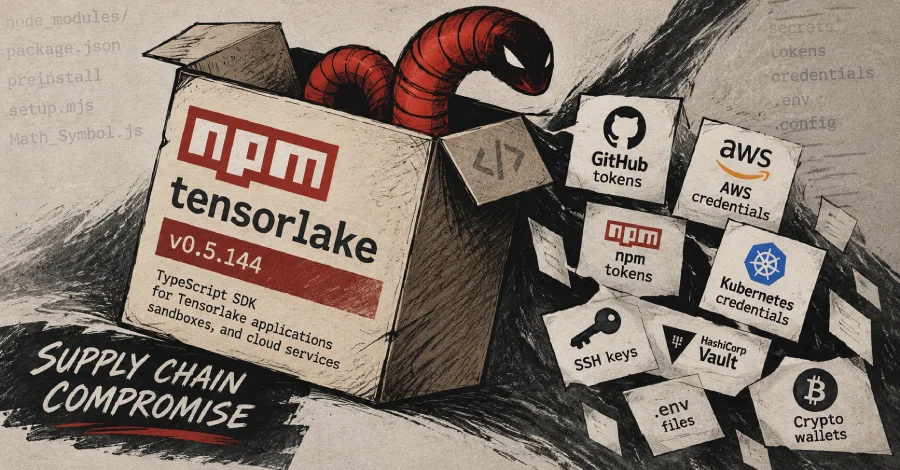
The npm package tensorlake, a TypeScript SDK for Tensorlake’s applications, sandboxes and cloud services, was compromised in a new wave of the ChainDrop / Shai-Hulud supply chain campaign. Version 0.5.144 contains a preinstall hook that downloads the Bun runtime and runs an obfuscated loader, which in turn launches a credential-stealing, self-propagating worm. Socket and StepSecurity both analysed the release; it is no longer downloadable from npm.
According to StepSecurity, the first malicious commit landed on the project’s main branch on October 7 under a maintainer’s name, and the repository’s own release workflow published 0.5.144 the next day, which is why npm shows a valid provenance attestation for it (provenance says where a package was built, not that the code is safe). The worm harvests npm and GitHub tokens, AWS keys, Kubernetes and Vault secrets, SSH keys, .env files, crypto wallets and configuration files for AI coding tools such as Claude, Cursor, Kiro, Windsurf and Zed. To spread, it republishes packages tied to the victim’s publishing identity and plants files (.claude/settings.json, .vscode/tasks.json) so it runs again when a project is opened in Claude Code or VS Code. A “hostage token” component watches the stolen GitHub token and, if the victim revokes it, runs code that StepSecurity says deletes the home directory. This is the ChainDrop campaign first seen in August, now reaching AI agent infrastructure.
How to check if you’re affected
Affected versions: only tensorlake@0.5.144 on npm. Pin the package to 0.5.143 (the version StepSecurity recommends) and search your lockfiles, CI caches and developer machines for 0.5.144. The preinstall hook skips CI, so developer machines are the main target; if it only ran in CI, rotate the secrets that job could see anyway.
If a machine installed it, do not revoke tokens first. StepSecurity says to remove the token monitor before rotating credentials, because revoking while it runs triggers the wipe. Indicators of compromise from the report:
- Files
~/.config/gh-token-monitor/and~/.local/bin/gh-token-monitor.sh - Network traffic to
iseekaigogo[.]com - GitHub repositories described “Shai-Hulud: Here We Go Again” and commits from
claude@users.noreply.github.com - Unexpected
.claude/or.vscode/files in your repositories
If you cannot be sure the machine is clean, StepSecurity recommends wiping it and starting fresh, then rotating every secret it could reach.