
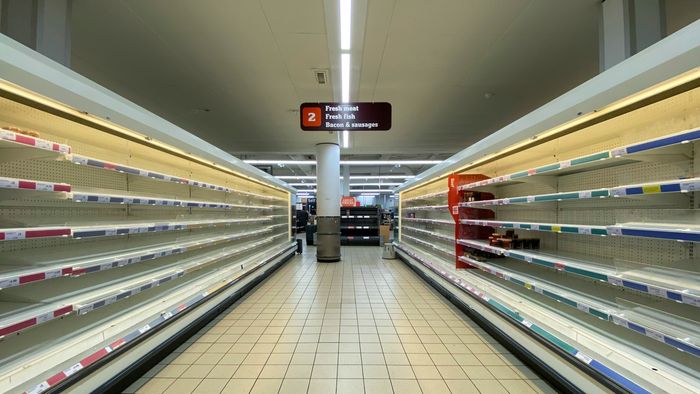
Overnight on Sunday, attackers remotely switched refrigeration systems into defrost mode at supermarkets across France, according to BleepingComputer and French outlets. The attack reportedly targeted Danfoss refrigeration controllers running older versions of the vendor’s control software, and the built-in automatic defrost function was used to raise temperatures in display units. Intermarché, Coopérative U, Carrefour Market, Monoprix, Leclerc and Super U are among the chains named, with French media putting the number of affected stores at 250 to 350 and reporting significant food losses.
Intermarché said the attack hit a service provider that manages refrigeration systems and that products were pulled from affected units. Coopérative U’s president called the attack unprecedented. EU agriculture commissioner Christophe Hansen condemned it, and the Paris prosecutor’s office has opened an investigation that includes food losses and fires. How the controllers were compromised has not been disclosed. Context from earlier research: CISA warned in 2025 about an authentication bypass (CVE-2025-41450) and a command injection flaw (CVE-2025-41451) in the Danfoss AK-SM 8xxA series, which Claroty’s Team82 showed could lead to remote code execution on exposed management interfaces. Nothing yet links those flaws to this attack. Researcher Baptiste Robert found 2,752 Danfoss systems exposed online on Monday, 1,590 of them in France, and Shodan tracks more than 4,500. BleepingComputer notes there is no evidence of a link to the Ahold Delhaize incident announced the same day.
How to check if you’re affected
Affected products reported so far are Danfoss refrigeration controllers; operators in food retail should check whether any Danfoss AK-SM 8xxA management interface or other controller is reachable from the internet and compare the installed software version against Danfoss’s advisories for CVE-2025-41450 and CVE-2025-41451. Remove direct internet exposure (put the interface behind a VPN or firewall), and ask your refrigeration service provider which remote-access path it uses. For shoppers there is nothing to configure: affected stores pulled the products from the affected units.