
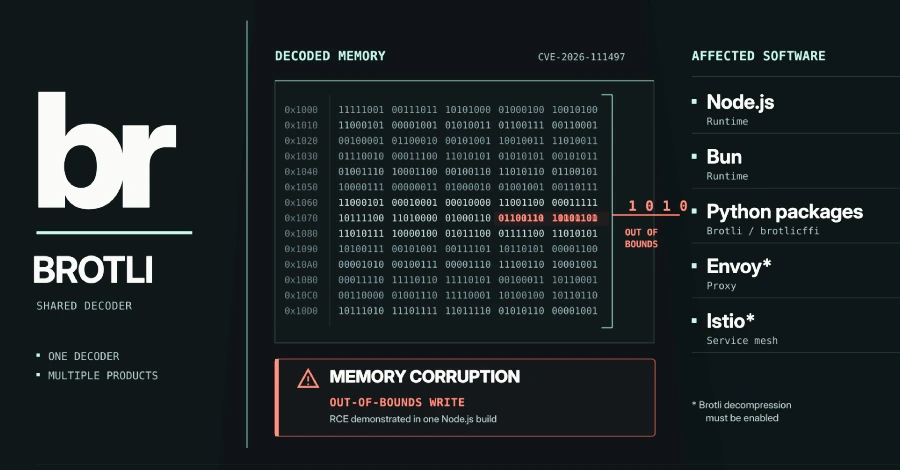
The memory-corruption flaw in Google’s Brotli decoder that we covered in the Node.js security release is not only a Node.js problem. Tracked as CVE-2026-111497, it lets specially crafted compressed data write past the end of a buffer, which can crash a program, leak memory or, potentially, run attacker-chosen code. Because each program ships its own copy of the decoder, The Hacker News reports that Bun, the Python Brotli and brotlicffi packages, Envoy, Istio and cdxgen are also affected and have to be updated one by one.
Imperva researchers showed code execution on one unpatched Node.js build; per The Hacker News the same has not been demonstrated on the other software, and no real-world attacks have been reported. A program is exposed only if it decodes Brotli data that someone else controls, for example a fetched web response sent with Content-Encoding: br. In Python, merely having either package installed lets HTTP clients such as requests, urllib3, httpx and aiohttp decode Brotli responses automatically, so an app can be exposed without importing Brotli itself. A web application firewall helps only partly: Vercel said its rules do not cover responses a function fetches from other servers, so the runtime or library has to be updated.
How to check if you’re affected
Affected versions and fixes, as tabulated by The Hacker News (check each vendor advisory for your exact build):
- Google Brotli C library: 1.0.3 to 1.2.0; fixed in 1.0.10, 1.1.1 and 1.2.1.
- Bun: 1.4.3 and earlier; fixed in 1.4.4.
- Python Brotli: 1.2.0 and earlier; fixed in 1.2.1. brotlicffi: 1.2.0.x and earlier; fixed in 1.2.1.0. Run
pip show brotli brotlicffiin each environment and container image. - Envoy: 1.39.2, 1.38.5, 1.37.7 and 1.36.11; fixed in 1.40.0, 1.39.3, 1.38.6, 1.37.8 and 1.36.12. Exposed only if the Brotli decompressor is configured.
- Istio: 1.31.0 to 1.31.1, 1.30.0 to 1.30.5 and 1.29.0 to 1.29.8; fixed in 1.31.2, 1.30.6 and 1.29.9. Exposed only if Brotli decompression is enabled.
- cdxgen standalone binaries and images: 13.4.0 and 12.8.8 and earlier; fixed in 13.5.0 and 12.8.9.
- Node.js: see the earlier post; fixed in 22.23.4, 24.22.1 and 26.12.1, and Node.js 20.x and older will not be patched.
Affected products also include anything else that bundles its own Brotli copy, so ask the vendor of such software for an update.