
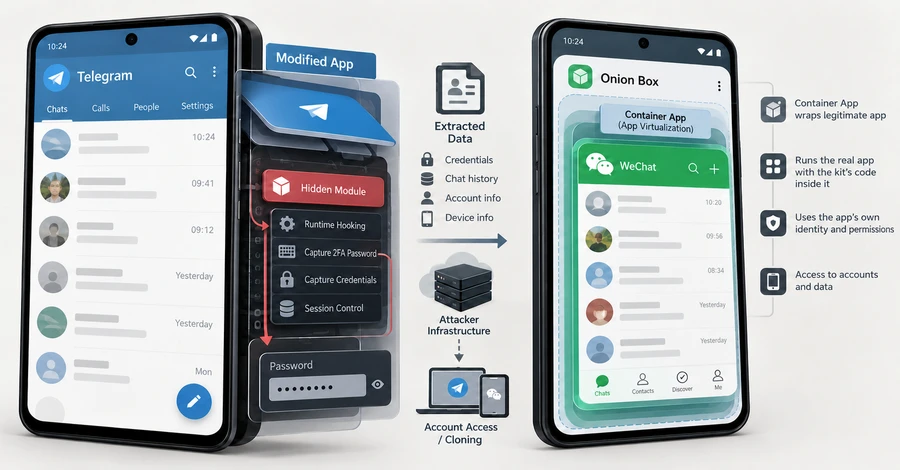
A rentable Android spyware kit called uCreator takes over Telegram and WeChat accounts by hiding its code inside working copies of the two apps, according to researcher Ovi, whose analysis was published on October 21, 2026. The Hacker News reports that the kit only reaches people who install one of these tampered copies, which spread outside the official app stores, or who run WeChat inside the kit makers’ own container app, called “Onion Box” (洋葱盒子). Ovi could not confirm how every victim was infected.
Inside a tampered Telegram app, the kit’s code runs with the app’s own identity and permissions, so it has the same access as the signed-in app. For WeChat, the kit can run the unchanged app inside its container, copy out the account’s login identity, upload the app’s data and use a bundled login script to clone the account. Ovi says the apparent targets, still unconfirmed, are users of mobile wallets and messaging apps in China and Southeast Asia, and that he found code supporting about 20 apps but published code only for Telegram and WeChat. He describes his report as “an analysis of technical capability, not a measurement of victim impact.”
The Hacker News compared the report with Doctor Web’s October 2025 write-up of Baohuo, a backdoor found in tampered copies of Telegram X. Doctor Web’s description of Baohuo lists the same code namespace (com.ucreator.tgjar), the same command server and matching command names as Ovi’s analysis, and Doctor Web estimated more than 58,000 infected devices at the time. Ovi’s report does not mention Doctor Web’s findings, and Doctor Web did not name the kit, so it is not clear whether the kit’s makers or one of their customers ran the Baohuo campaign. Ovi also reports that parts of the kit’s back end were exposed on a self-hosted GitLab server, and ties parts of the operation to three companies in Hunan province, China; he calls a shared owner “plausible, but remains unproven.”
How to check if you’re affected
Affected devices are Android phones with a Telegram or Telegram X copy that was installed from a downloaded app file instead of the official store, or with WeChat run inside the “Onion Box” container app. According to The Hacker News, some tampered Telegram X copies use the same package name as the real app on Google Play, so the name alone does not give them away.
Ovi calls two traces on a phone reliable: a code file named TgJarPine.dex in the assets of some tampered Telegram copies, and the original app copy that the off-the-shelf patching tool LSPatch leaves at cache/lspatch/origin/*.apk. The second can also appear in apps patched with that tool for other reasons. Doctor Web has published its own indicators for Baohuo. If you installed Telegram or WeChat from anywhere other than the official store, the cautious route is to reinstall the app from the official store; the sources do not give account-recovery steps, so check your Telegram active sessions and your WeChat login history for devices you do not recognise.
Sources
- uCreator: virtualization-based Android spyware platform targeting WeChat, Telegram and other messaging apps - Ovi, 0x0v1
- uCreator Android Spyware Can Steal Telegram 2FA Passwords and Clone WeChat Accounts - The Hacker News
- Baohuo, the gray eminence. Android backdoor hijacks Telegram accounts - Doctor Web, October 2025