
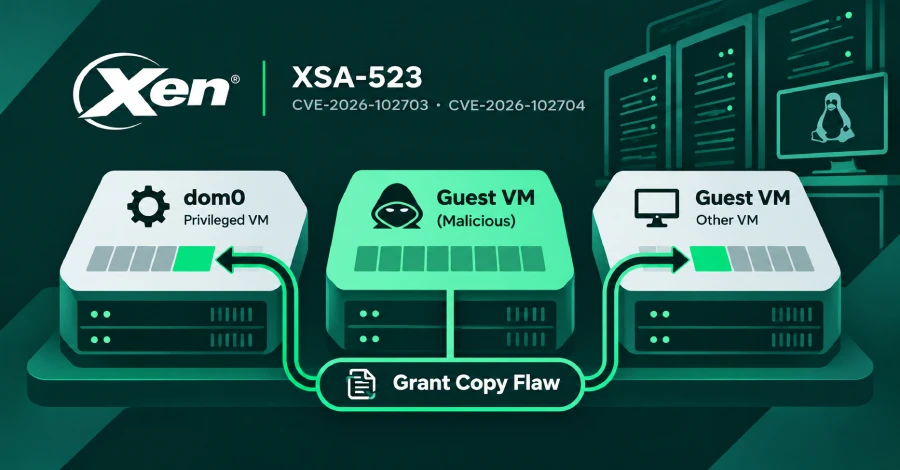
The Xen Project disclosed two flaws on November 3 that let a malicious guest virtual machine (VM) read and write the memory of other VMs on the same host, including dom0, the privileged VM that manages the rest. The advisory, XSA-523, tracks them as CVE-2026-102703 and CVE-2026-102704, and says there is no known mitigation. Patches are available.
The flaws sit in grant copy, the operation Xen uses to copy data between VMs. Per the advisory, Xen caches details to speed up batches of copies on adjacent address ranges in the same page, but did not re-validate them when it should have. In one case, frame numbers and grant references could be mixed up (CVE-2026-102703). In the other, the check that limits copying by frame number to the caller’s own memory was misplaced (CVE-2026-102704). The advisory’s stated impact is that a malicious guest can read and write arbitrary memory belonging to other domains, including dom0.
The Xen Project credited Anthropic with finding the flaws using its Claude model, with Stephan Lipp of Ada Logics validating the finding and the CodeAnt AI Security Research Team later reporting the same issue independently, according to The Hacker News. Neither the advisory nor The Hacker News’s report mentions attacks exploiting the flaws or says what access inside the guest an attacker needs. XCP-ng’s update notes, quoted by The Hacker News, say “a single compromised guest can break out of its isolation and take over the whole host.”
XSA-523 is separate from XSA-500, an earlier grant copy flaw Xen disclosed on July 28, and has its own patches.
How to check if you’re affected
Affected versions are all Xen releases from 4.6 onward; Xen 4.5 and earlier are not vulnerable. Products built on those versions are affected until their makers add the XSA-523 patches. Fixes published so far, per the advisory and The Hacker News:
- Xen source: the advisory has patches for xen-unstable through 4.19.x, and for 4.18.x and 4.17.x. It has no patch for 4.6 to 4.16; Xen 4.16’s security support ended on December 2, 2024.
- XCP-ng 8.3:
xen-4.17.7-4.2.xcpng8.3, released November 3. Hosts must be rebooted. Vates rates the impact Critical. - Qubes OS 4.3: Xen packages 4.19.6-3 in dom0, which must be restarted. Anti Evil Maid users must reseal their secret passphrase, because the new binaries change PCR18 and PCR19. Qubes says every supported release and configuration is affected, and tells users to keep installing updates as normal; the fixed packages were in its security-testing repository, due to move to stable after community testing.
- Debian: as of November 4, The Hacker News says Debian’s security tracker listed the xen package as vulnerable in bookworm, trixie and forky, and fixed in sid.
If you run Xen directly or through a product built on it, check your vendor’s advisory for the fixed package for your release and plan the reboot.