
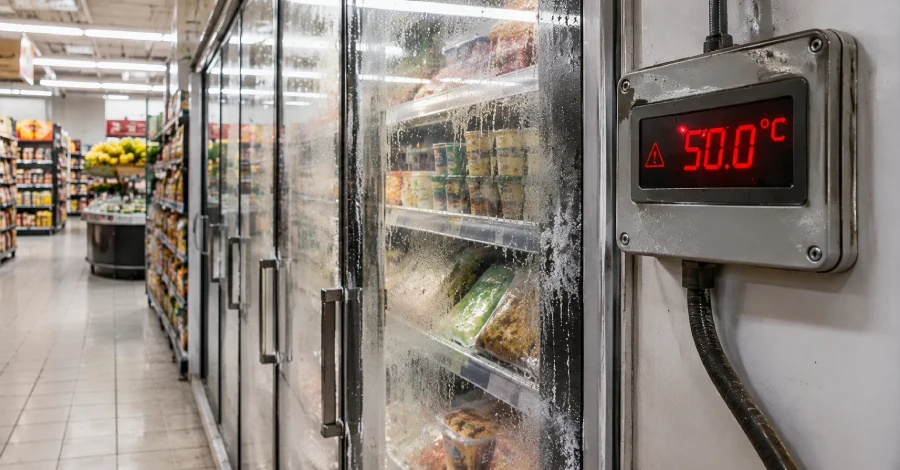
Five US agencies have issued a joint advisory saying threat actors are actively targeting industrial refrigeration and cold-chain monitoring systems around the world. CISA, the FBI, the Department of Health and Human Services, the Department of Agriculture and the Department of Transportation say attackers may use authentication bypasses, arbitrary code injection and weak configurations in unpatched or internet-accessible controllers to change settings remotely. That can force units into continuous heating and defrost cycles, causing inventory loss and equipment hazards, or cut off visibility into temperatures with a denial-of-service. The Hacker News, which reported the advisory, adds that altered temperatures can create a fire hazard or harm consumers who buy products after unsafe storage.
The advisory follows attacks on supermarkets that we have already covered: the October attack on French supermarkets and the second wave across Europe. According to The Hacker News, hundreds of supermarkets in Belgium, Estonia, Finland, France, Germany, Ireland, Italy, Luxembourg, the Netherlands, Portugal, Sweden and the UK were targeted in recent weeks, with temperatures raised as high as 50 degrees Celsius in some cases. The French Blood Establishment confirmed that an incident at a refrigeration equipment provider raised temperature and defrost settings to “extremely high levels” at three facilities storing blood plasma. It is unclear who is behind the attacks.
How to check if you’re affected
Affected products are internet-accessible industrial refrigeration and cold-chain monitoring controllers, and the advisory is aimed at their owners and operators. The two product families that Censys tracked after CERT-FR’s emergency alert are Danfoss StoreView and Copeland/Dixell XWEB; Censys counted 3,124 exposed hosts across them on 5 November, down from 6,695 on 9 October (708 StoreView and 2,420 XWEB).
- Find out which refrigeration, defrost and temperature-monitoring controllers at your sites can be reached from the internet.
- The agencies, as summarized by The Hacker News, urge owners to use strong authentication, keep systems updated, identify internet-accessible systems, isolate operational technology devices, change default passwords, retire and replace legacy devices, and remove or secure remote access.
- For Danfoss controllers, Censys notes that the earlier-disclosed CVE-2025-41450 (an administrator login derived from the current date) has been chained with other Danfoss flaws for remote code execution by Claroty researchers. Check the vendor’s advisories for the exact versions and fixes that apply to your model.
- If you run a shop or small business rather than the controllers themselves, asking your refrigeration supplier whether the equipment is reachable from the internet is a sensible first step (our suggestion, not the agencies’).
Sources
- The Hacker News: U.S. Agencies Warn Refrigeration Controller Attacks Could Cause Fires and Inventory Losses
- Censys: European Refrigeration Controller Exposure: A Second Attack Wave
- CISA’s news release and the joint advisory itself are linked from The Hacker News article but returned “Access Denied” to our checker, so they were not read directly; the advisory’s contents above are as reported by The Hacker News.