
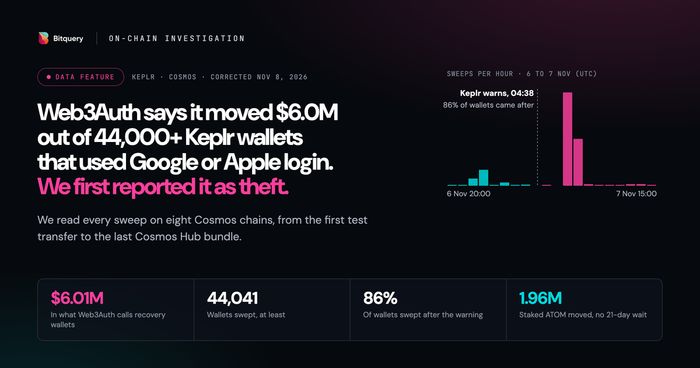
Some people who set up a Keplr crypto wallet by signing in with a Google or Apple account have had money stolen. Keplr relies on a company called Web3Auth to run that sign-in, and both companies said late last week that an attacker used a security flaw at Web3Auth to reach the wallets. Keplr described it as a “private key breach” for some of those users. Web3Auth then used the attacker’s own route to empty other at-risk wallets before the attacker got to them, according to The Hacker News, moving the money with the wallet maker’s help into recovery wallets for safekeeping. That means an empty balance may mean the money was rescued, not stolen.
Neither company has said how the flaw worked, when the attacker first used it, or whether that route is now closed. No official dollar figure for the theft exists: GoPlus, a Web3 security firm, said at least about $1 million had been stolen without explaining its figure. The blockchain-data firm Bitquery counted at least $6.01 million moving from more than 44,000 Keplr wallets into the recovery wallets, and corrected its first analysis, which had read those transfers as the theft; it says it cannot confirm who controls the recovery wallets. Web3Auth has not said how or when the rescued funds will be returned. It has also said the issue affects services used by some other companies, but Keplr is the only one it has named. It said its first investigation found no evidence that MetaMask users are affected. Consensys, MetaMask’s maker, bought Web3Auth in June 2025.
How to check if you’re affected
Affected products are Keplr wallets created with Google or Apple sign-in. Keplr says wallets made with a recovery phrase or a hardware wallet are not affected. It has paused Google and Apple sign-in while it investigates, and the Web3Auth status page lists a Login Service maintenance event starting 6 November that cites a security incident.
Keplr’s guidance for accounts created with Google or Apple login, as quoted by The Hacker News:
- Do not send new funds to the account.
- Do not re-import or recreate the account anywhere.
- Move any funds that are not staked or locked to an account that uses a recovery phrase or a hardware wallet. Staked and locked assets are taking longer to secure.
- Trust updates only from the official accounts of Keplr and Web3Auth, and ignore direct messages or links offering “recovery”.
Keplr and Web3Auth are working on a way for users to check whether their account was affected. Meanwhile Web3Auth has published a list of its recovery addresses so people can tell its transfers from possibly malicious ones, and it warned against assuming that an unfamiliar destination address belongs to the attacker.
Sources
- The Hacker News: Web3Auth Flaw Exploited to Steal Keplr Crypto, Provider Empties Other Wallets for Safety
- Bitquery: Keplr Wallet Hack: Web3Auth Says It Secured $6.0M (on-chain analysis, corrected on 8 November after its first version read the transfers as theft)
- Keplr statement on X (the opening text was readable; the rest is as quoted by The Hacker News)
- Web3Auth status page
- Web3Auth’s incident update, recovery thread and address list, and the GoPlus alert, are linked from The Hacker News article and were not read directly.