
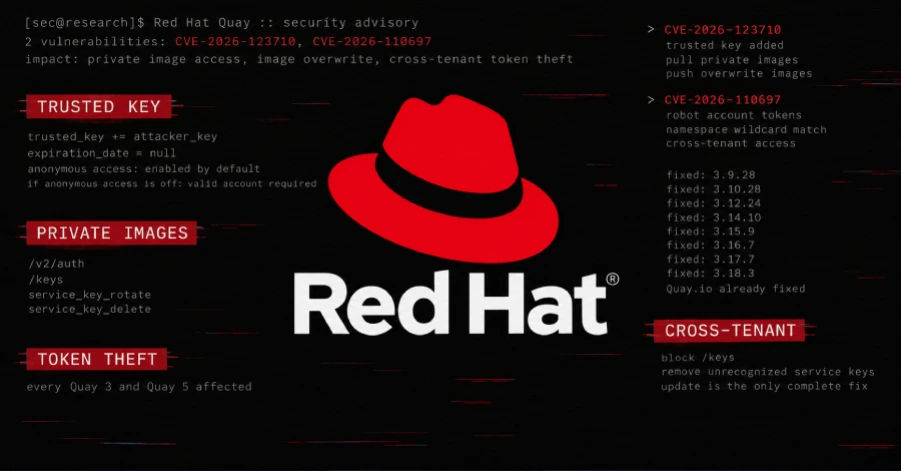
Red Hat has fixed two critical flaws in Quay, its container registry, that let an attacker read and overwrite private container images. The Hacker News reports that Red Hat published the advisories on November 11 and that its own engineer, Dave O’Connor, found both. None of the sources we read reports attacks in the wild.
The first, CVE-2026-123710 (CVSS 9.8), is in Quay’s key server. Quay signs the access tokens that authorize image pushes and pulls with keys it trusts, and Red Hat says the key-rotation endpoint checks only that a request carries a token signed by an approved key with the expected audience and issuer, not that the token was issued for rotation. An anonymous token from Quay’s /v2/auth endpoint passes that check, and the caller chooses its audience. The result, per Red Hat, is that an unauthenticated client can install its own signing key with no expiry and then forge tokens that work on any repository. Anonymous access is on by default; Red Hat stresses that turning it off does not protect you, because any valid Quay account can still exploit the flaw. With a planted key an attacker can pull private images and any secrets stored in them, push or overwrite images that every later pull will receive, or delete the keys running instances use so normal pushes and pulls fail. Red Hat adds that the key survives restarts and that resetting passwords or regenerating robot tokens does not revoke it.
The second, CVE-2026-110697 (CVSS 9.9 per The Hacker News), is a tenant-isolation flaw. Red Hat says the code that lists robot accounts builds a database search pattern from the namespace name without escaping wildcards, so a user who can create a namespace containing an underscore can match another tenant’s namespace and read its robot accounts’ decrypted tokens. Those tokens can then be used to read, push or overwrite that tenant’s images. Red Hat notes that where Quay is the integrated registry for OpenShift, stolen robot credentials could be used to inject malicious images into CI/CD pipelines. This one needs an account that can create a namespace, but not elevated privileges or any action by the victim.
How to check if you’re affected
Affected products are Red Hat Quay deployments reachable by untrusted clients: standalone installs, Quay deployed by the Quay Operator on OpenShift, and the mirror registry for Red Hat OpenShift, including internal registries. The Hacker News says Red Hat lists every Quay 3 and Quay 5 version as affected by both flaws. Red Hat’s page for CVE-2026-110697 lists the fixed releases as 3.9.28, 3.10.28, 3.12.24, 3.14.10, 3.15.9, 3.16.7, 3.17.7 and 3.18.3, and says Quay.io is already fixed. The Hacker News says Red Hat released fixed builds for eight Quay 3 branches and that each advisory lists CVE-2026-123710, but that none of the eight advisories lists CVE-2026-110697. The Red Hat page for CVE-2026-123710 that we read did not list versions, so confirm your branch’s fixed release in Red Hat’s advisory before relying on this list.
For CVE-2026-123710, Red Hat’s mitigation steps are to block the /keys endpoint at your proxy or load balancer for everything except trusted internal components, then search the audit logs for service_key_rotate and service_key_delete events where expiration_date is null and remove any approved service keys you do not recognize. Red Hat is explicit that deleting a rogue key is not durable until a fixed build is running, because the same anonymous request can plant a new one. The pages we read do not say whether the fixed release removes a key that was already planted, so auditing for unrecognized keys after updating as well is our suggestion, not Red Hat’s.
For CVE-2026-110697, Red Hat says updating is the only complete fix. If you cannot update at once, it suggests limiting who can create organizations or namespaces with an underscore in the name, rotating robot tokens for any namespace that could collide with an underscore namespace, and watching for pulls or pushes that do not fit normal robot use. Red Hat says these steps reduce exposure but do not fix the flaw. The Hacker News notes that the CVE record for CVE-2026-123710 still showed every Quay package as affected with no fix when it checked, even though each advisory lists the flaw.
Sources
- Red Hat: CVE-2026-123710
- Red Hat: CVE-2026-110697
- Red Hat: Identifying and remediating unauthorized signing keys in Red Hat Quay (CVE-2026-123710; the full remediation steps are subscriber-only)
- Red Hat Bugzilla 2568072: CVE-2026-123710
- Quay upstream commit: Fix CVE-2026-110697 and CVE-2026-123710 (#8056) (linked from The Hacker News; we read only its title, and the description of the fix comes from The Hacker News)
- The Hacker News: Critical Red Hat Quay Flaw Lets Attackers Read and Overwrite All Private Container Images in a Registry