
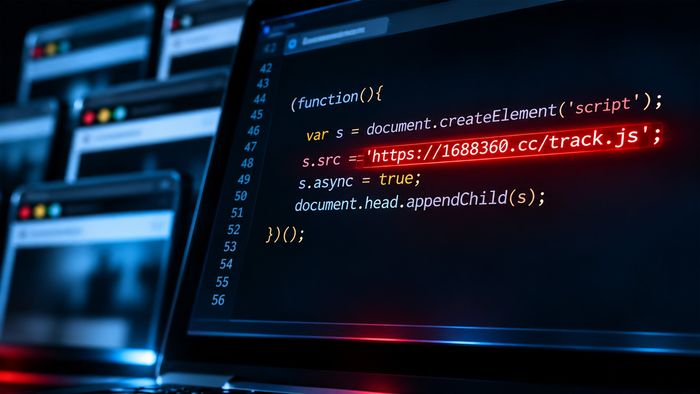
On November 16, 2026, visitors to a long list of well-known websites were served malicious JavaScript without the sites themselves being hacked. BleepingComputer reports that attackers exploited a vulnerability in the Experimentation account signup flow of Optimizely, a platform many companies use to test and personalize their web pages, and used it to add malicious code to customer projects. Optimizely confirmed this to BleepingComputer and said it has blocked the vulnerable path, deployed a fix, removed the injected code from affected projects, ended active sessions, revoked tokens and reset access for affected accounts.
Security researcher Scott Helme of Report URI, a vendor that sells script-monitoring tooling, counted 188 infected Optimizely script files belonging to 178 organizations, and BleepingComputer confirmed the malicious script loaded, or tried to load, on sites including Zoom, KLM, GitLab, BBC, CNN, Salesforce, Fox News, Air France, HSBC Insurance and Bitly. The injected code loaded a script from 1688360[.]cc that, per Helme’s analysis, swaps cryptocurrency wallet addresses for the attacker’s, skims card numbers typed into pages, collects cookies and screenshots, and on iPhones and iPads loads the Coruna and DarkSword exploit kits. Helme reported about $7,040 had reached the attacker’s wallets as of 19:25 UTC on November 16; BleepingComputer notes some of those wallets were active before this attack, so the total stolen by this campaign is hard to pin down. Helme also wrote that it is not known how the attacker got write access to so many unrelated customer projects; that is for Optimizely to explain.
How to check if you’re affected
Affected devices are any phone, tablet or computer that loaded a page from a site using Optimizely Web on November 16, 2026. Helme’s guidance for visitors, from his Report URI write-up:
- Update iPhones and iPads to iOS 18.7.3 or later, or iOS 26.3 or later. His analysis says the exploit kit’s own comments list those releases as patched, and that on iOS 18.6 or earlier a page reloads every 60 seconds as it retries the exploit.
- Check any crypto transfer made that day: if the address that was pasted does not match the one you meant to pay, it may have been swapped.
- Watch card statements if you paid by card on an affected site.
If you run a site that uses Optimizely Web, Helme advises opening every project’s Project JavaScript and each experiment’s custom code and looking for 1688360.cc, atob( and any script you did not write; reviewing who and what has write access to your Optimizely account and rotating credentials; treating cards entered on November 16 as potentially exposed; and deploying a Content Security Policy. Block the attacker domains he lists (1688360.cc, 5vobauua3ojpklx.icu, eil786npto9u5bq.icu, l7bcsnwc7nzr3uo.icu and webshell.lol, including subdomains).
Helme’s write-up said at 21:52 UTC on November 16 that only 1 of the 188 infected snippets still carried the code, down from 169 earlier. Salesforce told BleepingComputer it was disabling Optimizely scripts across its preview and production instances as a precaution while it investigates. Optimizely says it is continuing to investigate and will post updates on its status page.
Related earlier coverage on the iOS kit: P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Theft.