
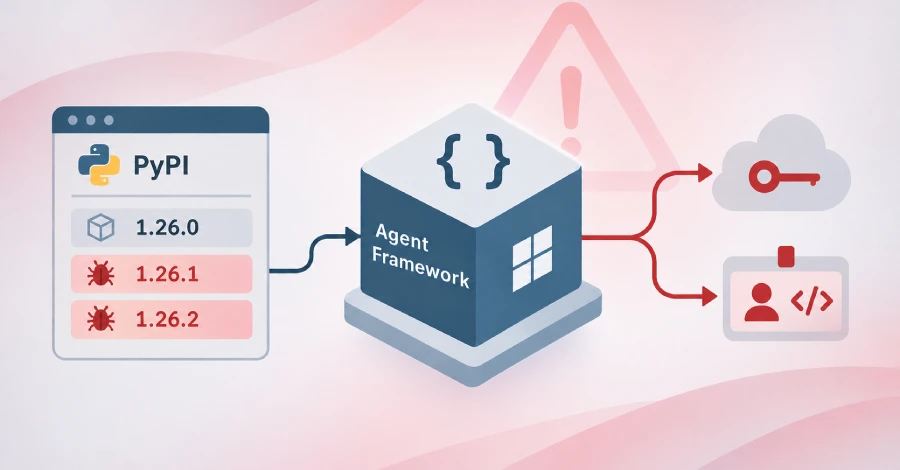
Attackers published two malicious versions of agent-framework, the meta-package for Microsoft’s open-source Agent Framework for building AI agents in Python, to PyPI on November 17. The Hacker News, citing reports from Aikido, Chainguard, Endor Labs, OX Security, SafeDep, Socket, StepSecurity and Wiz, says versions 1.26.1 and 1.26.2 were published 33 minutes apart and have since been removed from PyPI. SafeDep’s timeline (UTC) shows 1.26.1 at 20:35 and 1.26.2 at 21:08, and 1.26.0 as the last clean release. The package gets about 190,000 downloads a month; how many installs the bad versions received is not known.
Each malicious wheel adds a .pth file to Python’s site-packages directory, so the stealer runs every time Python starts in that environment, even if nothing imports the package. SafeDep says it collects environment variables and credential files (Azure CLI, .npmrc, pip.conf, .netrc, .git-credentials, Docker and Hugging Face configs) and also asks Azure DevOps, Azure managed identity and, in 1.26.2, GitHub Actions for fresh tokens, then sends everything to a webhook.site address. Because it requests new tokens, SafeDep notes that rotating stored secrets does not cover those. It is unclear how the attacker got publishing access. SafeDep says a second PyPI maintainer, vibiret, was created on the day of the attack and can publish to agent-framework and five related projects; it says the join date points to that account but that neither PyPI nor Microsoft has released the upload log that would confirm it.
How to check if you’re affected
Affected versions are agent-framework 1.26.1 and 1.26.2. Any machine, container image or CI runner that installed either one between roughly 20:35 and 21:20 UTC on November 17, 2026 (The Hacker News gives the exposure window as about 8:35 to 9:20 p.m. UTC) should be treated as affected.
- Search lockfiles and requirement files for
agent-frameworkat 1.26.1 or 1.26.2. SafeDep gives agrep -rnE 'agent[-_]framework.{0,20}1\.26\.[12]\b'command for this. - Look for
agent_framework_meta.pth(1.26.1) oraf_runtime_diag.pth(1.26.2) in site-packages without starting that environment’s Python, since starting it would run the stealer again. - Search proxy and DNS logs for requests to webhook.site, including the address The Hacker News lists.
- SafeDep says to treat every secret reachable from an environment that installed either version as exposed, including Azure CLI sessions, Azure DevOps tokens and service connections, and tokens for PyPI, npm, NuGet, Docker, Hugging Face and git. Rotate them from a clean system, then review sign-in and activity logs for managed identities and federated credentials that environment could use, as The Hacker News and SafeDep both advise.
- Pin to 1.26.0. SafeDep also advises locking the whole dependency tree with hashes and holding off on new releases of agent-framework and its five sibling projects until Microsoft removes the extra maintainer and confirms they are clean.
None of the pages we read carried a statement from Microsoft.