
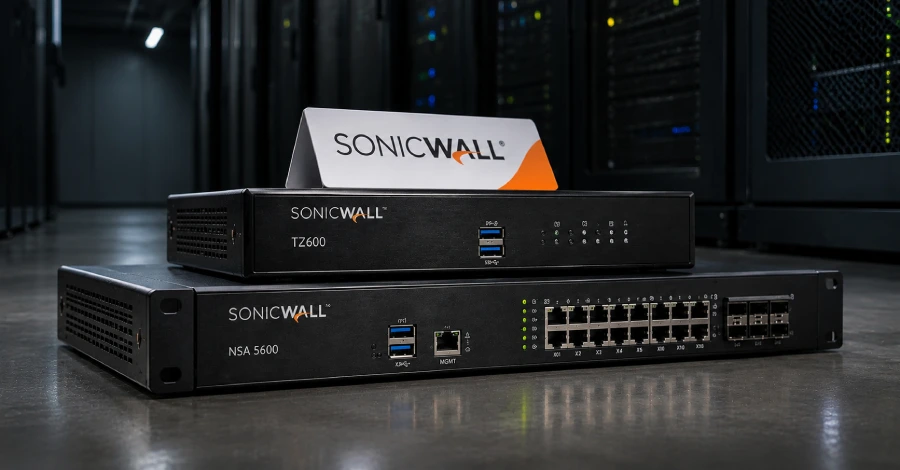
SonicWall has urged every customer still running a Generation 6 firewall to retire and replace it immediately and to stop exposing it at the internet edge. Per The Hacker News, SonicWall says Gen 6 hardware no longer receives security patches, even for critical flaws, and that it expects internet-facing Gen 6 firewalls to be actively targeted. Its advice is to treat any Gen 6 firewall still in service as a high-risk exposure and migrate to a supported Gen 8 firewall running SonicOS 8.
SonicWall’s reasoning, as quoted by The Hacker News, is that attackers now use automation and AI to find and exploit unsupported edge devices faster than ever. The article backs that up with two outside reports: Google Mandiant’s M-Trends 2026 report puts the mean time to exploit at an estimated -7 days, meaning exploitation on average begins before a patch exists, and Cisco Talos’ 2025 Year in Review found that 23% of CVEs discovered in the year directly affect network devices such as VPN appliances and firewalls, according to the article. The article does not give an end-of-support date for Gen 6, and it does not describe any specific attack on these devices.
How to check if you’re affected
Affected products are the Gen 6 firewalls running SonicOS 6.x. The Hacker News lists these models:
- TZ350, TZ350W, TZ500, TZ500W, SOHO 250 and SOHO 250W
- TZ400, TZ400W, TZ600, TZ600P and TZ300, TZ300W, TZ300P
- SOHO and SOHO W
- NSA 2600, NSA 3600, NSA 4600, NSA 5600 and NSA 6600
- NSa 2650, NSa 3650, NSa 4650, NSa 5650, NSa 6650, NSa 9250, NSa 9450 and NSa 9650
- NSv 10 to NSv 1600 (Gen 6 virtual firewalls)
- SuperMassive 9200, 9400, 9600 and 9800
- NSsp 12400 and NSsp 12800
SonicWall’s recommended steps, as relayed by The Hacker News, are to inventory every Gen 6 firewall in production and retire them, starting with units exposed to the internet or providing remote access, then replace them with Gen 8 firewalls running SonicOS 8 and contact an authorized SonicWall partner to plan the migration. Until a unit is replaced, SonicWall advises:
- Disable WAN management (HTTPS, SSH and SNMP on WAN interfaces).
- Disable SSL VPN, or restrict it to known source addresses.
- Enforce multi-factor authentication on every remaining remote-access and admin account, and reset local passwords.
- Disable services and interfaces that are not in use.
- Monitor logs closely for unusual logins, configuration changes and traffic.
SonicWall’s advisory page returned only a small script shell when we fetched it, so the model list and steps above come from The Hacker News’s account rather than the advisory text itself.
Sources
- SonicWall product advisory: retire unsupported Gen 6 firewalls (linked from The Hacker News; page did not render, not read directly)
- The Hacker News: SonicWall Warns Gen 6 Firewalls Won’t Get Security Patches, Even for Critical Flaws
Related earlier coverage of another end-of-life SonicWall product: SonicWall Won’t Patch Two Flaws in End-of-Life GMS Software.